Author: Munim

Munim is a contributor at Cyber Snowden, writing about cybersecurity careers, threats and technology for readers who want clear, practical explanations.

Quantum Cryptanalysis

Introduction Quantum cryptanalysis represents a paradigm shift in cybersecurity, challenging the very foundations of classical cryptographic systems. As quantum computing continues to evolve, its ability to solve complex mathematical problems exponentially faster than classical computers poses both unprecedented risks and opportunities. What is Quantum Cryptanalysis? Quantum cryptanalysis is the study of cryptographic algorithms in the presence of quantum-enabled adversaries. It leverages the power of quantum computing to break traditional encryption methods, exploiting algorithms like Shor’s and Grover’s to compromise public-key and symmetric-key cryptosystems, respectively. Core Quantum Algorithms in Cryptanalysis Shor’s Algorithm: Targets public-key cryptography, including RSA, ECC, and DSA. Efficiently…

Read More
Supply Chain Attack Vectors

Introduction In today’s interconnected digital ecosystem, supply chain attack vectors have emerged as a significant cybersecurity threat. These attacks target the weakest links in a supply chain, exploiting vulnerabilities within third-party vendors, software dependencies, and even insider threats. As organizations increasingly rely on complex supply chains, understanding these attack vectors becomes imperative to safeguarding sensitive data and maintaining operational integrity. What Are Supply Chain Attack Vectors? Supply chain attack vectors refer to the various pathways through which cybercriminals can infiltrate an organization by targeting less secure elements within its supply chain. These vectors can compromise software, hardware, and service providers,…

Read More
Hardware Trojan Detection

Introduction In today’s interconnected world, the security of integrated circuits (ICs) is paramount. As design houses increasingly outsource fabrication to untrusted foundries and incorporate third-party intellectual property (IP) cores, the risk of hardware Trojans (HTs) has surged. HTs can alter IC functionality, reduce reliability, leak sensitive information, and even cause denial of service. Their detection is vital for safeguarding critical infrastructure, military systems, and consumer electronics. This comprehensive guide delves into hardware Trojan detection methods, explores emerging threats, and discusses advanced prevention strategies. Understanding Hardware Trojans A hardware Trojan is a malicious modification within an IC that can compromise its…

Read More
Steganographic Malware

Introduction In the evolving landscape of cybersecurity threats, steganographic malware stands out as one of the most insidious and stealthy forms of cyberattacks. By leveraging the ancient art of steganography—the practice of concealing information within seemingly innocuous files—cybercriminals can embed malicious code into images, videos, audio files, and even website scripts without raising suspicion. This article delves deep into the mechanisms, real-world examples, and preventive measures surrounding steganographic malware. What is Steganographic Malware? Steganographic malware utilizes steganography to hide malicious code within ordinary digital files. Unlike cryptography, which scrambles data to prevent unauthorized access, steganography’s primary goal is to conceal…

Read More
Biometric Data Breaches

Introduction In an increasingly digital world, biometric authentication—using fingerprints, facial recognition, voice patterns, and iris scans—has revolutionized identity verification. While it offers unparalleled security and convenience, biometric data breaches present alarming risks. Unlike passwords, biometric data can’t be reset once compromised, posing lifelong threats to individuals’ privacy and security. This article explores the vulnerabilities of biometric systems, real-world breach incidents, privacy concerns, and strategies for mitigating risks in an era dominated by AI and surveillance technologies. What Is Biometric Data? Biometric data includes unique physiological and behavioral traits used for authentication and identification. Common types include: Fingerprints: Digital mapping of…

Read More
Cyber Warfare

In the rapidly advancing digital era, cyber warfare has emerged as one of the most significant threats to global security. Unlike traditional warfare, cyber warfare operates in the unseen realm of cyberspace, where nations, organizations, and non-state actors engage in hostile activities to disrupt, damage, or manipulate critical systems. This article delves into the essence of cyber warfare, its attack methods, notable examples, and effective defense strategies. What Is Cyber Warfare? Cyber warfare refers to the use of digital attacks by one nation-state (or affiliated groups) against another to cause disruption, espionage, or sabotage. These attacks target government systems, critical…

Read More
Secure Access Service Edge

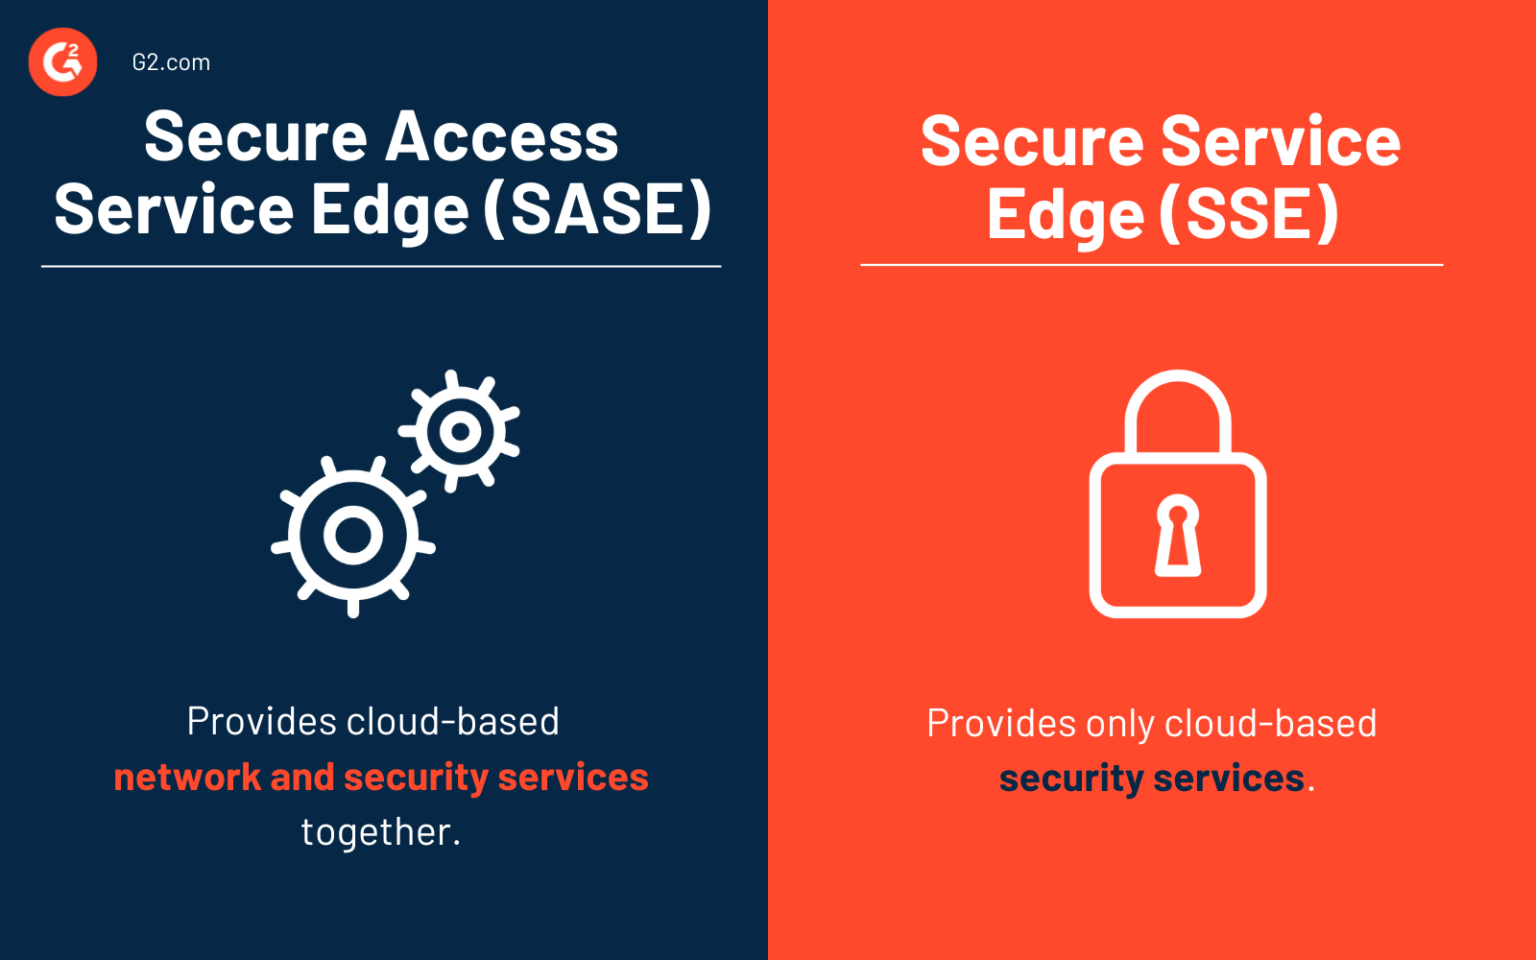
The shift to cloud-first operations and hybrid workforces has blurred traditional network security boundaries. Enter Secure Access Service Edge (SASE) and Security Service Edge (SSE)—two frameworks revolutionizing how organizations secure distributed environments. Yet, confusion persists: Is SSE just a subset of SASE? When do you need one over the other? This article demystifies both models, their use cases, and how they align with SD-WAN integration, network-as-a-service (NaaS), and hybrid workforce demands. Defining SASE and SSE What is SASE? Secure Access Service Edge (SASE) combines networking and security into a unified, cloud-delivered service. Defined by Gartner in 2019, SASE merges SD-WAN…

Read More
Low-code automation

As organizations grapple with escalating cyber threats and regulatory pressures, traditional IT risk management approaches struggle to keep pace. Enter low-code automation—a game-changer that empowers citizen developers (non-technical users) to build intelligent workflows, streamline compliance, and mitigate risks. However, without proper governance, these tools can introduce new vulnerabilities. This article explores how low-code bridges intelligent automation with IT risk management, its transformative use cases, and the pitfalls to avoid. The Rise of Low-Code in IT Risk Management Low-code platforms (e.g., Microsoft Power Apps, OutSystems, Appian) enable drag-and-drop app development, reducing reliance on overburdened IT teams. Gartner predicts that by 2025,…

Read More
Zero-day attacks

As cyberattacks become more advanced, traditional security tools struggle against zero-day exploits—undiscovered vulnerabilities that bypass standard defenses. In 2023, zero-day attacks increased by 35%, with AI-driven techniques aiding attackers in evading detection. To combat this, businesses are adopting AI-powered threat hunting, utilizing machine learning (ML), behavioral analytics, and the MITRE ATT&CK framework to proactively find and stop these advanced threats. The Rise of Zero-Day Attacks and Traditional Security Gaps Zero-day attacks exploit undisclosed flaws, leaving no preparation time for defenders. Legacy tools like signature-based antivirus are ineffective, as they rely on known threat patterns. Traditional methods fall short due to:…

Read More
Cybersecurity for SMEs

Small and medium-sized enterprises (SMEs) must invest in cybersecurity to guard against phishing and other cyberattacks. Is your business prepared? Cybersecurity is now a critical concern in today’s markets. The growth and survival of your business could be at stake, as a cyberattack can have severe consequences. Beyond paying a ransom, an attack can lead to: Business operations coming to a halt; Legal disputes; Loss of trust with clients and partners. No organisation is immune: in 2019, 71% of Canadian businesses experienced cyberattacks that impacted their operations. This statistic only includes reported incidents. Protect Yourself from Phishing and Data Theft…

Read More