

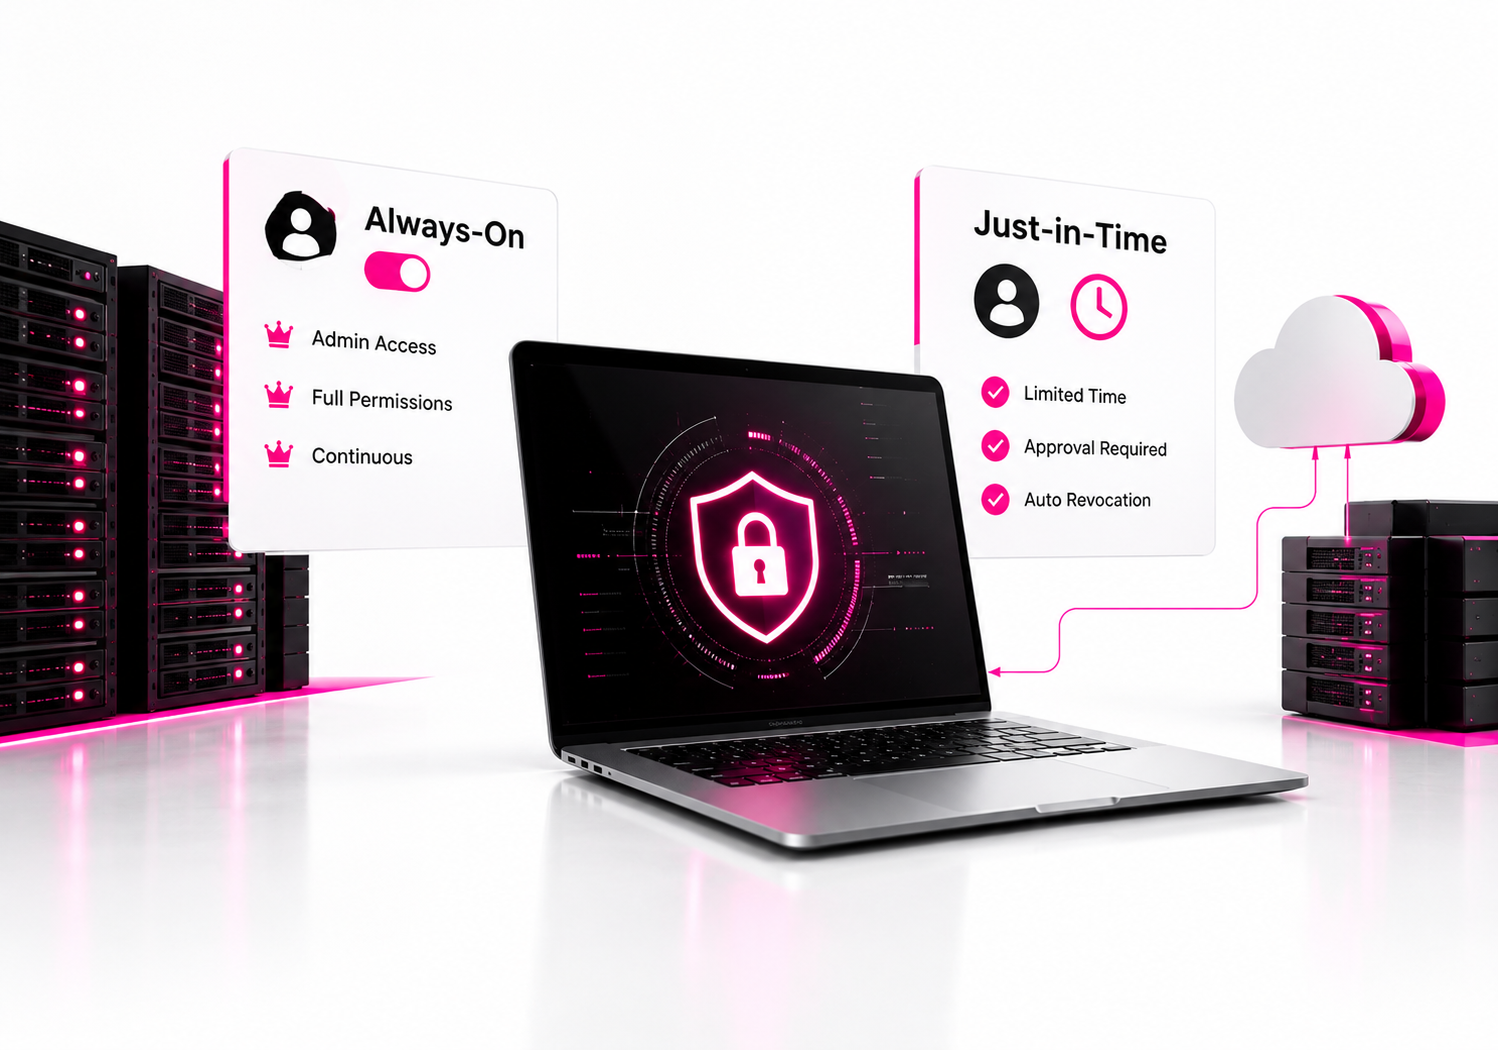
Just-in-time access is generally more secure than always-on privileged access because it limits elevated permissions to the time and task that require them. Always-on privileges leave powerful accounts continuously available, increasing the opportunity for credential theft, misuse, and accidental changes. JIT access reduces that standing-privilege exposure while preserving administrative access when it is actually needed.
The difference is straightforward: with always-on privileges, an administrator may have elevated permissions every minute of every day. With just-in-time (JIT) access, that administrator is normally eligible for the privilege but activates it only when required, often for a limited duration and sometimes with MFA, approval, or a business justification.
That model fits the broader zero-trust principle of granting access based on the resource and current need rather than assuming that a user should retain broad access indefinitely. NIST’s Zero Trust Architecture guidance explicitly shifts the security focus toward protecting resources rather than trusting users or systems because of their network location.
What is the difference between just-in-time access and always-on privileges?
Just-in-time access grants privileged permissions temporarily when a specific task requires them, while always-on privileges remain active regardless of whether the user is currently performing privileged work.
Consider a cloud administrator who needs to modify a production firewall rule.
With always-on access, the administrator might permanently hold a highly privileged Azure, AWS, or Google Cloud role. The permission exists before, during, and after the maintenance task.
With JIT access, the administrator could have an eligible role instead. They request activation, complete required controls such as MFA or approval, receive the privilege for a defined period, make the change, and then lose the elevated permission automatically.
| Access model | How it works | Main risk |
|---|---|---|
| Always-on | Privilege remains active continuously | Larger exposure window |
| JIT | Privilege activates temporarily when needed | More operational complexity |
Microsoft’s cloud security benchmark explicitly recommends avoiding standing access for user accounts and using JIT mechanisms for privileged permissions instead.
Why are always-on admin privileges risky?
Always-on privileges create a standing attack opportunity: if a privileged identity is compromised while its elevated permissions are active, an attacker may immediately inherit those permissions.
The problem is not limited to malicious employees. Credentials can be stolen through phishing, malware, token theft, compromised endpoints, session hijacking, or other identity attacks.
An always-on Global Administrator account is especially concerning because the attacker does not have to wait for the victim to request additional permissions. The privilege is already attached to the identity.
There is also an accidental-risk problem. A legitimate administrator can make a destructive change while working under a highly privileged account simply because the account already has permissions that exceed the immediate task.
CISA recommends separately managing privileged accounts with privileged access management and specifically identifies just-in-time provisioning as a way to temporarily grant elevated access for a task. CISA also recommends time-based access for administrative accounts.
How does just-in-time access reduce security risk?
JIT access reduces the amount of time a privileged permission is active, which can reduce the window in which stolen or misused credentials can exercise that privilege.
Suppose an administrator needs a powerful role for a 30-minute maintenance operation.
Under an always-on model, the privilege might be available for the other 23.5 hours of the day as well. Under JIT, the elevated permission can be limited to the maintenance window.
That does not make the account immune to compromise. If an attacker compromises the administrator during the activation period, the attacker may still be able to abuse the privilege.
JIT is therefore a risk-reduction control, not a replacement for MFA, endpoint security, session monitoring, strong authentication, logging, or least-privilege role design.
Microsoft’s documentation makes this distinction useful: PIM provides time-based and approval-based role activation, MFA, justification, notifications, access reviews, and audit history. These controls add friction around privileged operations without permanently removing the administrator’s ability to perform them.
Is just-in-time access part of Zero Trust?
Yes, JIT access strongly supports zero-trust security because it replaces implicit, persistent privilege with access that is explicitly requested, evaluated, and limited to a defined need.
NIST SP 800-207 describes zero trust as an architecture in which there is no implicit trust based on physical or network location and access to resources is granted when the resource is required.
JIT fits naturally into that model.
The important distinction is that zero trust is much broader than JIT. A company cannot become zero trust simply by turning on a privileged-access feature. Identity verification, device posture, resource protection, policy enforcement, segmentation, logging, and continuous evaluation all matter.
JIT should therefore be treated as one control inside a larger identity and access strategy.
What are the benefits of JIT privileged access?
The main benefits are reduced standing privilege, shorter exposure windows, better auditability, and stronger control over sensitive administrative operations.
Reduced standing privilege
Users can remain eligible for an administrative role without continuously possessing the role’s permissions.
That is a meaningful difference. Eligibility is not the same as active privilege.
Smaller exposure window
A compromised account with no active elevated role has fewer opportunities to immediately perform privileged actions than an account that permanently holds administrative permissions.
Better accountability
A mature JIT workflow can require the administrator to provide a reason for activation and can record when the privilege was activated.
That creates useful evidence for incident investigation and compliance reviews.
Stronger approval controls
High-risk roles can require another person to approve the activation request.
For example, a production database administrator might be allowed to activate a read-only role independently but require approval before activating permissions that allow destructive changes.
Automatic expiration
The privilege can expire without relying on an administrator to remember to remove it manually.
That is one of JIT’s biggest practical advantages.
What are the disadvantages of just-in-time access?
JIT access introduces operational complexity, and poorly designed workflows can frustrate administrators or encourage teams to create insecure exceptions.
A developer who needs an emergency production permission should not have to wait 45 minutes for an approval chain while a service is failing.
That is why JIT deployments need sensible emergency procedures, appropriate activation durations, reliable automation, and clear ownership.
There is also a configuration problem. If the underlying role grants excessive permissions, making it temporary does not fix the excessive privilege itself.
A 30-minute Global Administrator session is still extremely powerful.
The best design combines least privilege + JIT, rather than using JIT as an excuse to keep oversized roles.
How does JIT compare with always-on access?
JIT is generally the stronger security model for privileged human access, while always-on access can still be appropriate for carefully designed low-risk roles and certain technical identities that genuinely require continuous permissions.
| Factor | JIT access | Always-on privilege |
|---|---|---|
| Security exposure | Lower standing exposure | Higher standing exposure |
| Administrator experience | Requires activation | Immediate access |
| Auditability | Usually stronger | Depends on logging |
| Operational complexity | Higher | Lower |
| Best use | Sensitive privileged operations | Carefully scoped persistent needs |
The goal should not be to eliminate every permanent permission.
A help-desk employee may need a persistent role that allows password resets. A monitoring service may need continuous read-only access to specific telemetry. Removing those permissions every few minutes would add complexity without necessarily providing meaningful security improvement.
The focus should be on standing high-impact privileges.
When should organizations use JIT access?
Organizations should prioritize JIT for high-impact administrative roles that can modify identity systems, production infrastructure, security controls, financial systems, or sensitive data.
Good candidates include:
- Cloud subscription or account administrators
- Microsoft Entra Global Administrators
- Production infrastructure administrators
- Domain administrators
- Security platform administrators
- Database administrators with write or destructive permissions
- Privileged access to sensitive SaaS applications
- Roles capable of changing authentication or authorization policies
For lower-risk access, permanent assignments may be reasonable if they are tightly scoped and regularly reviewed.
A useful rule is simple:
If compromising the account would give an attacker a major ability to change the environment, strongly consider making that privilege eligible rather than permanently active.
How does Microsoft Entra PIM implement JIT access?
Microsoft Entra Privileged Identity Management (PIM) lets organizations make users eligible for privileged roles and require activation before those roles become active.
An administrator can configure controls such as:
- MFA during activation
- Business justification
- Approval requirements
- Maximum activation duration
- Notifications
- Access reviews
- Audit history
Microsoft distinguishes between eligible and active assignments. An eligible user can activate the role when needed, while an active assignment gives the user the role’s permissions without requiring activation.
This distinction is central to a good JIT design.
For example, instead of keeping a security engineer permanently active as a highly privileged role, the organization can make the engineer eligible. When an incident occurs, the engineer activates the role, completes the investigation, and the elevated access expires.
How does Google Cloud handle temporary privileged access?
Google Cloud supports temporary access patterns through IAM conditions and Privileged Access Manager, allowing organizations to move away from permanent high-privilege access.
Google Cloud’s Privileged Access Manager supports just-in-time, time-bound, and approval-based access elevations. Entitlements can specify who is eligible, which IAM roles are granted, the resource scope, the duration, and whether approval or justification is required.
Google also documents temporary access using IAM Conditions, which can grant expiring access to cloud resources.
This is useful for teams operating across multiple cloud environments because the same principle can be applied even though the implementation details differ between providers.
How should you implement just-in-time access?
Start with your highest-risk standing privileges, reduce the role scope, then add time limits, MFA, approval, logging, and automatic expiration.
A practical rollout looks like this:
1. Inventory privileged access
Export your current privileged identities and identify users, groups, service accounts, and roles with administrative capabilities.
Do not focus only on obvious “admin” accounts. Custom roles and nested groups can create significant privilege as well.
2. Find standing high-impact permissions
Prioritize permissions that can:
- Create or delete identities
- Change authentication policies
- Disable security controls
- Modify production systems
- Access sensitive data
- Change network boundaries
- Grant additional privileges
3. Reduce the role itself
Before converting an always-on role to JIT, ask whether the role is already too broad.
A temporary excessive privilege is still excessive.
4. Convert permanent assignments into eligible access
Make users eligible for the role where the platform supports that model.
For Microsoft environments, this is commonly handled through Microsoft Entra PIM.
5. Require strong activation controls
Use MFA and, where appropriate, approval and business justification.
CISA’s guidance specifically recommends JIT access as part of privileged access management and emphasizes limiting elevated access to specific needs and timeframes.
6. Set reasonable activation durations
Do not automatically grant eight hours of administrative access because the platform allows it.
If a routine operation normally takes 30–60 minutes, start with a duration close to that requirement. Provide a controlled extension process for unusual tasks.
7. Monitor activation and privileged activity
Record who activated the privilege, why it was activated, what resource was involved, and what actions occurred during the privileged session.
Activation logs alone are not enough. You also need logs from the protected systems.
8. Test emergency access
A JIT system that works perfectly during normal operations but fails during an outage becomes a liability.
Test emergency procedures and maintain tightly controlled break-glass accounts where necessary.
What should you do with service accounts and automation?
Do not blindly convert every service identity to human-style JIT access; automated workloads often need a different approach based on workload identity, short-lived credentials, scoped permissions, and credential rotation.
A backup service that runs every night may legitimately need access at scheduled times. A CI/CD pipeline may need deployment permissions only during releases.
Instead of giving those systems permanent broad credentials, consider workload identities, short-lived credentials, narrowly scoped roles, and automated credential expiration where supported.
The principle remains the same: give the workload only the permissions it needs, and avoid long-lived secrets whenever the platform provides a safer mechanism.
JIT is primarily valuable for reducing standing privileged access; it should not be treated as a universal answer to every identity problem.
Can JIT access prevent account compromise?
No. JIT cannot prevent an account from being compromised, but it can reduce the damage that compromised credentials can cause when privileged permissions are not continuously active.
If an attacker steals a user’s ordinary credentials, JIT may prevent immediate access to certain privileged resources because the elevated role is not active.
However, attackers can also target the JIT workflow itself. They may steal an authenticated session, compromise the administrator’s endpoint, abuse an approval process, or wait until the legitimate user activates the role.
That is why Microsoft warns that PIM/PAM controls do not address every privileged-access risk, including risks caused by compromised devices.
JIT should therefore sit alongside phishing-resistant MFA, hardened administrator workstations, endpoint detection, session logging, network controls, and strong identity governance.
FAQ: Just-in-Time Access vs Always-On Privileges
Is just-in-time access more secure than always-on access?
For high-impact privileged access, JIT is generally the safer model because elevated permissions exist only when required. It reduces standing privilege and can add MFA, approval, justification, expiration, and monitoring. However, JIT does not eliminate compromise risk and must be combined with strong authentication, endpoint security, least privilege, and logging.
What is an example of just-in-time access?
A cloud administrator may normally have no active production-admin permissions but remain eligible for the role. When a production issue occurs, the administrator requests activation, completes MFA and any required approval, receives the role for a limited period, performs the task, and automatically loses the elevated permission when the activation expires.
What is the difference between JIT and least privilege?
Least privilege determines how much access a user should have, while JIT determines when privileged access should be active. They work together rather than replacing one another. A strong design gives an administrator only the permissions needed for a task and makes those permissions available only for the period required.
Is JIT access part of Zero Trust?
JIT access strongly supports Zero Trust because it avoids treating privileged access as permanently trusted. Zero Trust requires broader controls around identity, devices, resources, policy, and continuous evaluation. JIT is therefore one practical mechanism for implementing least-privilege and resource-focused access decisions.
Does JIT eliminate the need for privileged access management?
No. JIT is commonly implemented as a capability within a broader PAM or PIM strategy. Privileged access management can also cover approvals, credential protection, session monitoring, access reviews, logging, and other controls. CISA specifically recommends PAM with JIT capabilities for managing privileged accounts.
Final verdict: JIT access vs always-on privileges
For sensitive administrative access, choose just-in-time access over always-on privileges whenever your technology and operational requirements allow it.
The security advantage is straightforward: a privileged account that is not currently privileged gives an attacker less standing authority to abuse.
But do not stop at the “enable JIT” checkbox. First reduce oversized roles, then enforce MFA, add approval where justified, set short activation periods, monitor privileged activity, and test emergency access.
The next step is to inventory every standing administrative role in your environment and identify the five privileges that would cause the most damage if stolen. Those are the best candidates for your first JIT migration.
